
Last Updated: October 13, 2026
Most teams treat segmentation as a VLAN exercise. That is the first mistake we see at Northwest Towers when we audit industrial networks.
Industrial network segmentation is the practice of dividing an OT network into isolated security zones connected only through controlled conduits. Each zone holds assets with similar trust levels and function.
Zone and conduit design for OT environments follows a simple logic:
CISA guidance on industrial control systems security recommends defenders map network architecture before writing a single rule. Do that first.
Port-based rules are a liability in OT. Modbus, DNP3, and OPC UA all run on well-known ports, and a rule that permits “TCP 502” from anywhere defeats the purpose of the firewall. The deeper problem is that a port-only rule cannot tell a legitimate read of a holding register from a write to a coil that changes a setpoint.
ICS firewall rules should specify source zone, destination zone, protocol, function code, and direction. A next-generation firewall that understands industrial protocols can inspect deeper than the port number. That inspection is what lets you allow the traffic a process actually needs while blocking the operations an attacker would abuse.
Industrial protocol inspection parses the payload, not just the header. The firewall reads the function code, the object or register reference, and the direction of the request, then compares that against the rule. Three protocols drive most of this work:
A practical rule shape looks like this: source zone, destination zone, protocol, permitted function codes, permitted direction, and a named owner. If a rule cannot be written in that shape, it is probably too broad.
Start every policy with a default-deny stance. Nothing crosses a zone boundary unless a documented rule allows it. Least privilege means each asset talks only to the systems it needs, on the protocols it needs, using only the function codes it needs.
Inspection is not free. Deep parsing adds latency, and some legacy controllers use vendor extensions or non-standard function codes that a firewall will flag as unknown. When that happens, the safe move is to isolate the device in its own zone with a narrow conduit rather than to disable inspection globally. Document every exception, give it an owner, and put it on the quarterly review list so it does not become permanent.
For the connectivity layer beneath these rules, a rugged industrial wireless product built for harsh environments keeps the zones reachable without adding fragile links that force you to widen a rule. rugged industrial wireless products | product page
An industrial DMZ architecture places a buffer network between IT and OT. Historians, jump hosts, and patch servers sit there, so no IT system touches a controller directly.
Auditors look for evidence that this boundary is enforced, logged, and reviewed. Keep the design simple: one DMZ, clear conduit rules, and an audit trail for every change. NIST Cybersecurity Framework frames this as part of the protect and detect functions, and it maps cleanly to OT.
Rules accumulate. A quarterly review keeps the policy honest and catches drift before an audit does.
A firewall rule review checklist turns a vague “we should clean this up” into a repeatable task. Pair it with rule recertification so every rule has a named owner.
Firmware updates fix vulnerabilities, but in OT they can also stop a line. Treat every update as a change with a rollback plan, and treat the maintenance window as a production decision, not an IT one.
| Phase | Action | Owner |
|---|---|---|
| Plan | Identify firmware release, known issues, and the specific vulnerability it addresses | Security |
| Test | Validate in a lab or staging zone with a copy of the production rule set | Engineering |
| Approve | Get operations sign-off on the window and the rollback trigger | Operations |
| Deploy | Apply in a scheduled maintenance window with a second engineer on standby | Network |
| Verify | Confirm rules, logging, and traffic match the pre-change baseline | Security |
| Close | Archive the old firmware, the old config, and the validation evidence | Security |
Two details separate an OT change from an IT change. First, the maintenance window should align with a natural process break, a shift change, a planned shutdown, or a low-demand period, rather than a fixed monthly slot. Second, the rollback plan must be tested, not just written. If the old firmware image and the old configuration are not both on hand and verified, the rollback is theoretical.
After the update, confirm the firewall still enforces the policy you expect. A short validation checklist:
A silent failure, logging stops, or a rule order shifts, is more dangerous than a visible outage because no one notices until an incident.
Some devices cannot be patched, cannot authenticate, and cannot be safely scanned. When that is the case, the firewall becomes the compensating control. Isolate the device in its own zone, restrict its conduits to the minimum protocol and function codes, and log every session. If the device only needs to talk to one historian, write one rule for that path and deny everything else. Document the exception with an owner and a review date so it does not become permanent by default.
Track a small set of operational KPIs so the program is provable at audit time: rule recertification coverage, stale-rule count, alert triage time, and policy-change failure rate. A policy-change failure rate that trends down over two quarters is stronger evidence than a completed update log.
Reliable connectivity underneath the change window matters as much as the change itself. A rugged industrial wireless product designed for harsh environments reduces the chance that a link failure during maintenance turns a planned update into an unplanned outage. rugged industrial wireless products | product page
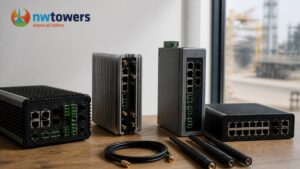
A firewall policy only works if the network underneath it is reliable. Northwest Towers designs and manufactures rugged industrial wireless products built for harsh environments, and we support them with network engineering, integration, deployment, and managed services, including Network as a Service.
For teams managing OT security, that means connectivity across mining, ports, construction, and utility sites without adding strain to a stretched IT team. Our monitoring services identify power, weather, and environmental anomalies before they become outages.
The hardest part of industrial firewall work is proving it works. Track rule count, blocked traffic, patch latency, and audit findings, then review those numbers quarterly.
If your OT network needs a connectivity foundation that holds up in the field, Northwest Towers can help. We offer rugged, IP-rated networking hardware, network design and audit services, and fully managed NaaS with little to no capital investment. Contact us to plan your industrial firewall deployment.
The strongest practices combine segmentation, protocol-aware rules, and disciplined change control. Start by dividing the OT network into security zones with an industrial DMZ between IT and OT. Write ICS firewall rules that understand Modbus, DNP3, and OPC UA rather than relying on open ports. Enforce default-deny and least privilege, then review rules on a fixed schedule. Finally, schedule firmware updates and configuration changes around production windows so uptime is never at risk.
A quarterly review works for most industrial sites, with an immediate review after any major network change, new asset deployment, or incident. Use a firewall rule review checklist that flags stale rules, shadowed rules, and any rule granting broad access. Document who owns each rule and why it exists. For sites with high change velocity, such as construction or mining projects, monthly reviews are reasonable. The goal is policy consistency, not review frequency for its own sake.
An IT firewall prioritizes confidentiality and typically inspects standard business protocols. An OT firewall prioritizes availability and safety, and it must understand industrial protocols like Modbus, DNP3, and OPC UA. OT firewalls also tolerate legacy systems that cannot be patched, support unidirectional gateways, and allow change control that avoids production downtime. The two environments need different rule philosophies, even when the underlying hardware platform is similar.
Begin by mapping assets into security zones: safety systems, control systems, supervisory systems, and enterprise IT. Place an industrial DMZ between IT and OT so no traffic crosses directly. Use conduits, which are controlled paths between zones, and enforce default-deny on every conduit. Apply least privilege so each zone reaches only the services it needs. Document the zone map and review it whenever new equipment or remote access is added.
Treat every rule change like a maintenance activity. Require a rollback plan, test in a lab or staging environment, and schedule the change inside an approved production window. Notify operations before the change and monitor for false positives afterward. Keep an audit trail of who approved the change and why. For legacy or unsupported assets, isolate them behind a dedicated zone rather than modifying rules on the live control network.
Industrial firewall practices only deliver results when the network beneath them stays online. Northwest Towers builds rugged wireless hardware and backs it with network design, monitoring, and managed services for demanding sites. Get started with Northwest Towers and give your OT security policy a connectivity layer it can depend on.